CS-OTH-ACC-001
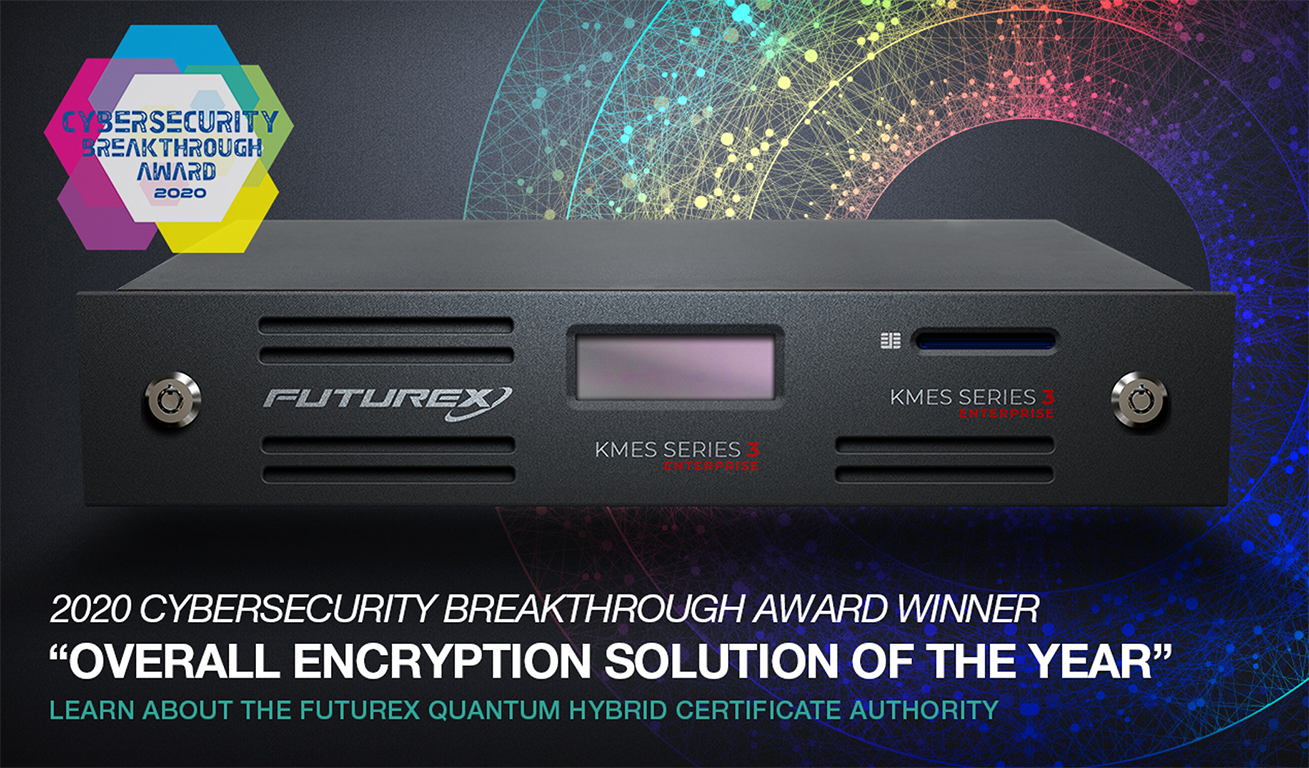
KMES Series 3
KMES Series 3 enterprise key-management solution.
A key-management platform for organisations managing sensitive cryptographic keys and related security workflows. Confirm the manufacturer, deployment architecture, integration options and supported versions.
Add to quote basketNo online checkout; tailored quotation.
Technical specifications
- Industry Compliance Standards Met
- FIPS 140-2 Level 3 EMVCo PCI DSS ANS X9.24 - Part 1 and Part 2 RoHS FCC Class B - Part 15 Applicable future compliance mandates
- EMV Certificate Management
- All major card brands supported Supports issuer self-signed certificate creation and export Creates ICC certificates according to EMVCo specifications
- KMES Series Unit Includes
- KMES Series 3 application CD KMES Series 3 documentation CD User guide Mounting brackets Two sets of two SCD barrel keys Cables
- Operating Conditions
- Power requirements: 100 - 240 VAC 50/60 Hz. 225 Watts Operating temperature: -40° to 140°F (-40° to 60°C) Storage temperature: -40° to 140°F (-40° to 60°C) Operating relative humidity: 20% to 80% non-condensing Storage relative humidity: 5% to 95% non-condensing
- Hardware
- Dual control-enabled\, tamper-responsive and evident design Smart card reader for M-of-N key fragmentation and dual-factor authentication Dual\, redundant gigabit Ethernet ports Dual\, redundant\, hot-swappable power supplies Automated\, internal RAID-based backup of object management application and databases
- Supported Key Types and Protocols
- DES Triple DES DUKPT X.509 v3 AES RSA EMVCo KMIP
- Security
- 2U hardened steel chassis with “Puzzle Box” tamper-resistant design Detachable front panel with two unique locks\, enabling dual control over front panel controls Versatile\, permission-based user system for enforcement of dual control and segregation of duties Software enforcement of split knowledge principles Battery-backed Secure Cryptographic Device (SCD) with epoxy barrier and tamper-responsive sensor wires
- Scalable Integration
- Capable of storing millions of keys and certificates Scalable to the Nth degree with multiple KMES devices centrally managed by the Guardian Series 3 Customized\, real-time monitoring and alerting via SMS\, SMTP\, and SNMP Automatic synchronization of objects with other KMES devices Object sharing with other Hardened Enterprise Security Platform devices and optional object segregation between remote applications
- Enterprise Application Encryption
- FIPS compliant security for application-based data protection Centrally manage the full key\, certificate\, and policy lifecycle Easy-to-use architecture simplifies and expedites deployment Segregated key containers\, enabling the creation of a single cryptographic resource pool for multiple independent applications Web-based workflow management for automation of key lifecycle tasks Standards-based libraries for easy integration: KMIP\, C# .NET\, Java
- Versatile Functionality
- Supports all common key types and protocols\, including DES\, Triple DES\, DUKPT\, X.509 v3\, AES\, RSA\, and EMVCo X9.17\, AKB\, and TR-31 (including custom optional fields) key block formats are available for use Encryption keys\, including major keys\, can be imported\, exported\, and backed up onto smart cards using M of N fragmentation Custom\, user-defined attributes and object grouping simplifying the management and organization process Supports mutual authentication under a trusted root certificate to establish a trusted public key infrastructure (PKI) Capable of generating and managing self-signed root certificates
- Model
- KMES Series 3